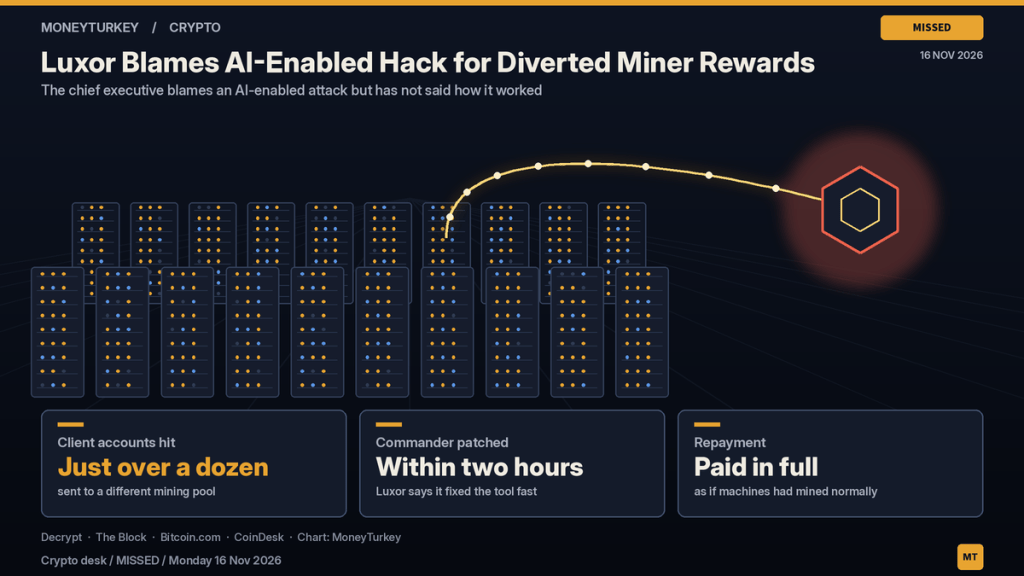
Hackers quietly steered the bitcoin miners of just over a dozen Luxor clients to another pool. The company blames an AI-enabled attack and promises full repayment.
MoneyTurkey Crypto desk | 16 November 2026
Key points
- Attackers used Luxor’s Commander fleet-management tool to point client machines at a different mining pool, so the rewards for their work went elsewhere
- Luxor says it patched Commander within two hours, no data was taken, and every affected client will be paid as if their machines had mined normally
- Chief executive Nick Hansen blames a “sophisticated AI-enabled vector” but has not said how the attack worked
Luxor Technology, a bitcoin mining software and services company, said on Sunday that its internal monitoring caught an unauthorised redirect of hashrate, the computing power miners use to secure the network and earn rewards. Just over a dozen client accounts were hit through Commander, the tool operators use to monitor their machines and change settings remotely, according to the company’s statements reported by Decrypt, The Block and Bitcoin.com.
How the hijack worked
Hansen said the compromise began around 6pm Pacific time on Saturday 14 November, Decrypt and CryptoSlate reported. The affected machines were pointed at OCEAN, a pool where miners combine their computing power and share the rewards, according to CoinDesk and CryptoSlate. Mining host CoreX Hosting was among the first to raise the alarm, both outlets said.
The trick needs no stolen wallet or private key. Changing a machine’s pool and payout settings is enough to send its earnings to someone else while the owner keeps paying for the electricity, CoinDesk noted. Hansen told The Block that the diverted hashrate was about 13 exahashes per second in total, in line with outside estimates cited by Bitcoin.com and CryptoSlate. He called it a highly visible incident rather than a major blow in bitcoin terms.
The AI defence
Hansen said businesses in crypto are now “inundated with AI-enabled attacks”, including from abliterated models, AI systems stripped of their safety guardrails, probing for weaknesses around the clock, Decrypt and The Block reported. Luxor has bought its own bare-metal graphics processors to run such models defensively. It has also put most new feature work on hold to rotate access keys, update systems and pin software dependencies, according to Decrypt and CoinDesk.
Why it matters
Luxor Pool and its LuxOS software were not affected, the company said, and Commander is running normally again. The bigger question is for every operator that manages machines remotely: if one tool can quietly reroute a fleet’s work, the cost of a breach lands on electricity bills, not on wallets. Luxor has not yet confirmed the outside estimates of how many machines were hit, and has promised a full post-mortem, Decrypt and CryptoSlate reported.
What to watch
- Luxor’s post-mortem and any detail on how AI was used in the attack
- Whether other fleet-management providers report similar redirects or tighten access
Related on MoneyTurkey
- Crypto movers: Lighter halts withdrawals after $15.5M drain
- Korea’s Upbit and Bithumb Freeze Lighter Token Transfers
- Strategy Adds Just 485 Bitcoin, Pours $228M Into Buybacks
For information only. Not investment advice.
Sources
- Decrypt: Hackers Redirected Bitcoin Miner Rewards via AI Attack, Luxor CEO Says
- The Block: Luxor hit by AI-enabled attack that redirected client hashrate
- Bitcoin.com: Luxor Confirms Bitcoin Mining Hack and Reveals AI-Enabled Attack
- CoinDesk: Bitcoin miners were hijacked and their rewards redirected to an attacker
- CryptoSlate: Bitcoin mining industry rocked by AI-linked breach

