Gnosis Pay disclosed unauthorised access to the legacy system behind its branded consumer cards and said customer funds were not affected.
MoneyTurkey Crypto Desk | 6 November 2026
Key points
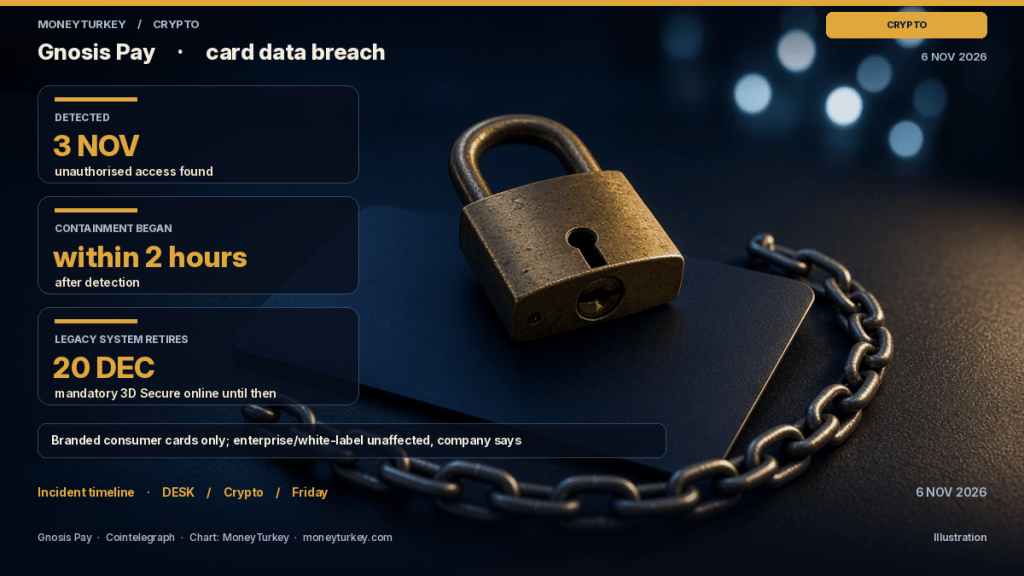
- Gnosis Pay detected unauthorised access to its legacy branded-card system on 3 November 2026; the company said containment began within two hours.
- The company said the legacy consumer system is already set to retire on 20 December 2026, with 3D Secure mandatory for online card payments until then.
Gnosis Pay said hackers gained unauthorised access to the system powering its branded consumer cards, resulting in the exposure of certain customer information. The company said it detected the intrusion on 3 November 2026 and that containment began within two hours. Gnosis Pay said customer funds were not affected and that its separate enterprise platform, which powers white-label card programmes, was unaffected.
What happened
In its 6 November disclosure, Gnosis Pay said it replaced compromised security credentials and addressed the vulnerability. The firm made 3D Secure verification mandatory for online card payments until the legacy B2C system retires on 20 December 2026. It also warned customers about phishing attempts and said it was arranging monitoring for potential misuse of the stolen data.
Cointelegraph reports that breach notifications it reviewed listed exposed categories including full payment card numbers, expiration dates, CVV codes, customer names, home addresses and linked wallet addresses. The notifications also listed email addresses, phone numbers, nationalities and, in some cases, IBAN and BIC banking details. Decrypt noted that Gnosis Pay’s public post did not specify what data was exposed.
One notification seen by Cointelegraph said that customer’s card was cancelled on 3 November, with no suspicious transactions or movement of funds detected for that account.
Scope and response
Gnosis Pay did not disclose how many customers were affected.
Gnosis Pay said customer funds remained safe despite the exposure of sensitive information, and stated that its separate enterprise platform was unaffected. The company said it had emailed every affected customer, reported the breach to partners and its card issuer, and was communicating with applicable data protection authorities.
Why it matters
The breach highlights the risks tied to legacy card systems that still hold customer credentials. Gnosis Pay’s decision to retire the consumer system on 20 December 2026 was already planned; the incident brought mandatory 3D Secure and stepped-up monitoring until that date. The company’s response focused on containment beginning quickly after detection, customer notification and added verification rather than a broader platform redesign.
What to watch
- Any follow-up disclosure on the number of affected customers
- Updates on phishing activity tied to the exposed data
- Progress on the 20 December 2026 legacy system retirement
Related on MoneyTurkey
For information only. Not investment advice.
Sources
- Gnosis Pay: https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards
- Cointelegraph: https://cointelegraph.com/news/gnosis-pay-breach-exposes-card-details-personal-data-crypto-wallet-information
- Decrypt: https://decrypt.co/382718/crypto-card-provider-gnosis-pay-hackers-customer-data

