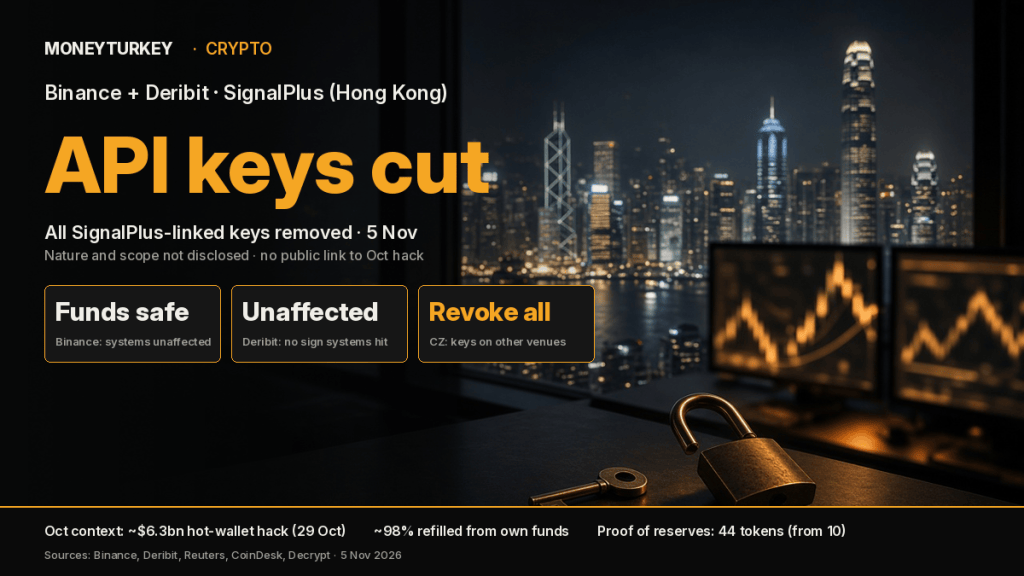
Binance and derivatives venue Deribit pulled every API key tied to SignalPlus after the Hong Kong options-tools platform flagged a potential security issue, a week after Binance’s record hack.
MoneyTurkey Crypto Desk | 5 November 2026, 14:05 London
Key points
- Binance removed all API keys linked to SignalPlus as an “immediate precautionary measure” after the platform reported a potential security issue; Deribit also removed SignalPlus keys.
- Binance said its own systems were unaffected and user funds remain safe; Deribit said it found no indication its systems or data were affected.
- Binance co-founder Changpeng Zhao told SignalPlus users to revoke their API keys on every other exchange too.
Binance said on Thursday it had removed every API key connected to SignalPlus, a Hong Kong-based provider of crypto options and derivatives trading tools, after SignalPlus reported a “potential security issue.” The exchange said its own systems were unaffected and user funds remain safe. Deribit, the crypto options exchange, said it had also removed SignalPlus-linked keys and found no sign its systems or data were affected.
API keys let third-party software place trades on a user’s exchange account without the user logging in each time. Cutting them stops any automated strategies running through SignalPlus on Binance until users set up new keys. Neither company has said what the suspected vulnerability is, how many users are affected, or whether any credentials were accessed.
What Binance told users
Binance told SignalPlus users to log in directly to review positions and open orders, and to wait until SignalPlus confirms the issue is resolved before reconnecting. It recommended IP whitelisting on all API keys, which limits a key to approved internet addresses, and asked every third-party platform integrated with the exchange to review its security controls and report unusual activity. Zhao went further on X: “If you use SignalPlus for any other exchange platform, it’s time to revoke all your API keys,” adding that users should generally avoid storing API keys with third-party platforms.
Why it matters
The scare lands on the options side of the market, where many institutional and active traders route orders across venues through Asian-built execution and analytics tools rather than exchange front-ends. A problem at one tool provider can expose connected accounts on several exchanges at once, even when the exchanges themselves are not breached and withdrawals are disabled on the keys. That is the gap Zhao’s warning targets.
It also comes at a sensitive moment for Binance. Attackers drained about $6.3 billion from its hot wallets on 29 October in the largest hack in crypto history, which the FBI has attributed to North Korean hackers it calls TraderTraitor; Pyongyang denies it. Binance has said the breach began when a fake recruiter persuaded an engineer to download malware. On Wednesday it said it had replenished about 98% of the stolen assets from its own funds and published a proof-of-reserves snapshot covering 44 tokens, up from 10. On Thursday it began reopening withdrawals for more assets in phases. There is no public link between the SignalPlus issue and the October hack.
What to watch
- A SignalPlus statement on the nature and scope of the issue
- Whether other exchanges connected to SignalPlus revoke keys
- Any unauthorised trading reported on affected accounts
- Binance’s phased reopening of remaining withdrawals
Related on MoneyTurkey
- Binance Says It Has Refilled 98% of Hacked Assets as Bitcoin Retakes $80,000
- Thailand SEC Moves to Block Bitget From Dec. 5 Over Unlicensed Trading
- South Korea Eyes 4th Crypto Tax Delay to 2029
For information only. Not investment advice.
Sources
- Binance statement on X, 5 November 2026 (via Decrypt): Decrypt
- Reuters via CNA: Binance, Deribit remove SignalPlus API keys after security issue
- CoinDesk: CZ warns crypto traders to pull SignalPlus API keys

